Free Cors Header Generator Online
Generate CORS response headers for allowed origins, methods, request headers, and credentials. Review your API policy before deployment.
100% private — generation runs in your browser. Never reflects Origin blindly; wildcard cannot combine with credentials.
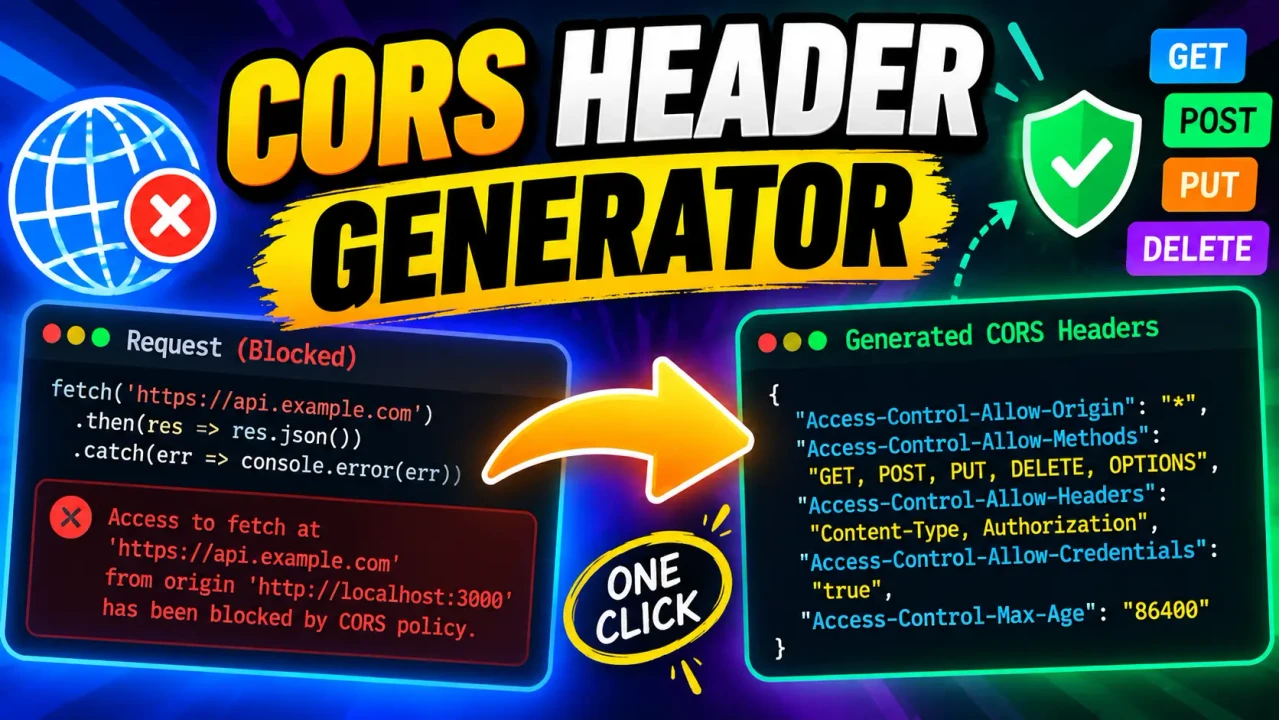
Free CORS Header Generator
Quick answer: Free CORS Header Generator is a developer utility for generating Cross-Origin Resource Sharing (CORS) response-header configuration. It helps turn CORS requirements such as allowed origins, HTTP methods, request headers, and credential handling into a header configuration that can be reviewed and applied to an API or web server.
TL;DR / Key Takeaways
- Primary Function: Generate CORS response-header configuration.
- Key Inputs: Allowed origins and CORS policy options.
- Core Output: HTTP CORS response headers.
- Best Suited For: API development, frontend integration, debugging, and configuration review.
What Is the Free CORS Header Generator?
Cross-Origin Resource Sharing (CORS) is the browser-controlled mechanism that determines whether frontend code from one origin can access resources returned by another origin. A server communicates its CORS policy through HTTP response headers such as Access-Control-Allow-Origin, Access-Control-Allow-Methods, Access-Control-Allow-Headers, and Access-Control-Allow-Credentials.
The Free CORS Header Generator provides a practical way to construct these response headers instead of assembling the policy manually. The generated configuration should be treated as a starting point: the final headers must match the routes, origins, authentication model, and HTTP methods actually used by the application.
How to Use Free CORS Header Generator?
- Choose the allowed origin: Specify the website or origin that should be permitted to access the resource. A wildcard may be appropriate for genuinely public, non-credentialed resources, while restricted applications generally need an explicit origin.
- Configure methods and headers: Select the HTTP methods and request headers required by the application, particularly when the browser performs a CORS preflight request.
- Configure credentials: Enable credential support only when the application actually needs cookies or other credentials. Credentialed CORS requires an explicit allowed origin rather than the
*origin wildcard. - Generate and review: Generate the headers, inspect the result, and then test the configuration against the real API and browser request flow.
Example CORS Configuration
Consider an API that should accept requests from https://app.example.com, permit GET and POST, and allow the client to send Content-Type and Authorization headers.
Example Input
- Allowed Origin:
https://app.example.com - Allowed Methods:
GET, POST - Allowed Headers:
Content-Type, Authorization - Credentials: Disabled
Representative Output
Access-Control-Allow-Origin: https://app.example.com
Access-Control-Allow-Methods: GET, POST
Access-Control-Allow-Headers: Content-Type, Authorization
The exact generated output should be reviewed against the options selected in the tool and the CORS requirements of the destination server.
CORS Header Reference
| Header | Purpose | Typical Value |
|---|---|---|
Access-Control-Allow-Origin |
Specifies which origin may access the response. | https://app.example.com or * for eligible non-credentialed use |
Access-Control-Allow-Methods |
Lists HTTP methods permitted for CORS access, particularly during preflight. | GET, POST, OPTIONS |
Access-Control-Allow-Headers |
Lists request headers permitted for the actual cross-origin request. | Content-Type, Authorization |
Access-Control-Allow-Credentials |
Indicates whether the response may be exposed when credentials are included. | true |
Access-Control-Expose-Headers |
Allows selected response headers to be exposed to browser JavaScript. | X-Request-ID |
Access-Control-Max-Age |
Controls how long a browser may cache the result of a preflight request. | 86400 |
These relationships follow the CORS model defined by the Fetch standard and documented by MDN. See MDN's CORS documentation and the WHATWG Fetch Standard for protocol-level details.
How CORS Headers Work
For a simple cross-origin request, the browser sends an Origin request header. The server's response can use Access-Control-Allow-Origin to indicate whether that origin is permitted to access the response.
More complex requests can trigger a CORS preflight request using the OPTIONS method. The browser can identify the intended method with Access-Control-Request-Method and requested non-safelisted headers with Access-Control-Request-Headers. The server answers with the corresponding CORS permission headers.
For example, a preflight response can contain:
Access-Control-Allow-Origin: https://app.example.com
Access-Control-Allow-Methods: GET, POST
Access-Control-Allow-Headers: Content-Type, Authorization
When an application uses credentials, the configuration needs additional care. A credentialed CORS response cannot use * as the value of Access-Control-Allow-Origin; the server must identify the permitted origin explicitly and use Access-Control-Allow-Credentials: true when appropriate.
Common CORS Edge Cases and Limitations
- Wildcard with credentials:
Access-Control-Allow-Origin: *is not valid for credentialed access. - Missing methods: A preflight can fail when the requested method is absent from the permitted method set.
- Missing request headers: A preflight can fail when the browser requests a header that the server does not permit.
- Multiple origins:
Access-Control-Allow-Origindoes not represent an arbitrary comma-separated list of origins. Applications supporting an allowlist normally need server-side origin matching and an appropriate response for the requesting origin. - Credentials and security: Credentialed cross-origin access should be limited to origins that genuinely require it. Broad CORS policies can expose application responses to unintended websites.
- Preflight versus actual request: A successful preflight does not by itself guarantee that every application request will succeed. The actual response must also satisfy the browser's CORS checks.
Supported Use
- Creating CORS response-header configurations.
- Reviewing allowed origins, methods, headers, and credential settings.
- Preparing configurations for API and frontend integration.
- Investigating common CORS configuration problems.
Limitations
- The generated headers do not automatically change the configuration of your API, reverse proxy, CDN, or web server.
- A generated policy does not guarantee compatibility with every server framework or deployment environment.
- CORS configuration should be tested in the actual browser and application environment where it will be deployed.
- Permissive CORS settings should not be treated as a substitute for authentication or authorization.
Related Technical Guidance
MDN recommends limiting Access-Control-Allow-Origin to the minimum origins and resources required by an application. The Fetch Standard defines the browser's CORS protocol and credential checks. These references are useful when reviewing a generated policy before production deployment.
Technical Disclaimer: Generated CORS headers are configuration guidance. Always validate the resulting policy against the application's authentication model, exposed resources, browser behavior, and server configuration before deploying it.
Author: Daniel Mercer — Software Engineer specializing in web platforms, HTTP APIs, browser security, and developer tooling.
Technical Review: Daniel Mercer reviewed the CORS terminology, header relationships, credential constraint, preflight behavior, and configuration guidance for alignment with established web-platform documentation.